The Director's Checklist for Executive and Enterprise Resilience
Archive

NACD Northern California
Contact Us
Lisa Spivey,
Co-Executive Director
Kate Azima,
Co-Executive Director
programs@northerncalifornia.nacdonline.org
Find a Chapter
About The Event
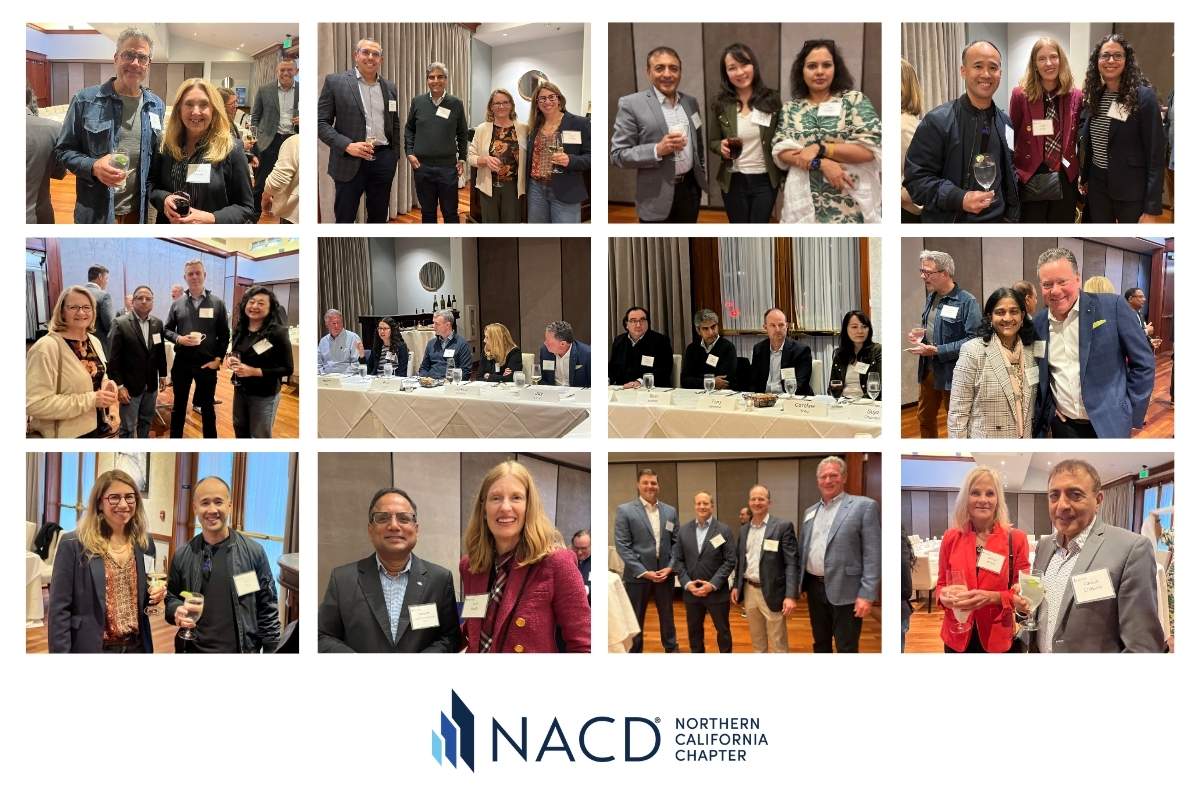
Boards today face a broader definition of resilience than ever before. NACD Northern California brought together a select group of directors and senior executives for a candid dinner on the board’s role in overseeing enterprise resilience. The conversation moved past traditional cybersecurity oversight toward a wider view that includes business continuity, technology dependencies, AI governance and physical security.
The discussion featured insights from Venkat Lakshminarayanan, John Pearce, Tony Perazzo, Rob Sloan and Erick Turasz.
KEY TAKEAWAYS
Board Oversight and Committee Structure
- Cybersecurity has historically sat within the audit committee, but expanding AI and technology risks are stretching already crowded agendas.
- Dedicated technology risk committees continue to emerge as a way to provide deeper oversight, although separating these issues can also create silos.
- Cybersecurity and AI should remain responsibilities of the full board, with clear accountability and information sharing across committees.
- Board composition and refreshment should consider whether directors have sufficient technical expertise to oversee AI, cybersecurity and innovation.
- Questions for the board: Does our committee structure provide adequate oversight? Do we have the right expertise? Are we discussing these risks frequently enough?
Moving from Cybersecurity to Business Resilience
- Boards need to shift their focus from preventing every cyberattack to ensuring the business can withstand disruption, contain threats and recover quickly.
- Technology risk extends beyond cybersecurity to legacy infrastructure, operational systems, products, customers and third-party dependencies.
- Four critical areas of resilience are AI-powered defense, technology debt, identity management and third-party risk.
- Zero trust architecture prevents lateral movement and contains the blast radius of an attack far more effectively than traditional network segmentation.
- Questions for the board: What does a credible resilience report look like? Could we maintain critical operations during an attack? How quickly could we contain and recover from a major incident?
AI and the Accelerating Cyber Threat Landscape
- AI is dramatically reducing the time and expertise needed to identify vulnerabilities and execute attacks, allowing adversaries to operate at unprecedented speed and scale.
- Legacy technology, including mainframes, manufacturing systems and medical devices, is increasingly exposed as AI makes previously difficult-to-identify vulnerabilities easier to exploit.
- The growing volume of vulnerabilities and required patches is putting pressure on security teams, resources and existing technology infrastructure.
- AI also offers significant defensive opportunities through automated threat detection, vulnerability management and faster incident response.
- Questions for the board: Are our defenses keeping pace with AI-enabled threats? How are we leveraging AI defensively? Are we investing enough to address technology debt and vulnerabilities? Do we have the right tools, and if so are they deployed correctly?
Agentic AI, Identity and Data Governance
- AI agents introduce new risks because they can independently access data, interact with systems and execute actions, often without traditional human oversight.
- Non-human identities require different security approaches, as agents operate continuously and do not follow predictable human behavior patterns.
- Shadow AI and third-party agents make it increasingly difficult for organizations to maintain visibility into what tools are being used and what information they can access.
- Zero trust principles (least-privilege access, continuous verification, and no implicit trust) apply equally to AI agents and non-human identities as to human users.
- Questions for the board: Do we know which AI agents are operating across our business? What data and systems can they access? Do we have a comprehensive AI risk program and clear accountability for agent behavior?
Balancing AI Innovation, Investment and Risk
- Boards must balance the competitive risks of moving too slowly on AI with the operational, legal and reputational risks of adopting it too quickly.
- AI adoption should be intentional, focused on clearly defined business opportunities, measurable outcomes and an understanding of where human involvement remains essential.
- AI-native organizations are increasingly designing workflows around agents first, with humans introduced at defined decision points.
- Traditional risk heat maps and investment assumptions may not reflect the speed at which AI-related risks are changing. Organizations need both the talent to implement AI effectively and the capabilities to govern it.
- Questions for the board: Where should we lean into AI, and where should we exercise restraint? Do we have the right talent? Are our investments proportionate to the risks and opportunities? How are we measuring success? Are we still experimenting, or implementing?
Third-Party Risk and Insurance Coverage
- Boards should understand the resilience of critical vendors and the potential business impact of a material outage or security incident.
- AI introduces additional exposures through autonomous agent behavior, data sharing, contractual terms and potential liability for inaccurate or harmful outputs.
- Cyber insurance policies are still evolving, and existing coverage may not adequately address emerging AI-related risks.
- Questions for the board: What is the security and AI posture of our key vendors? What happens if a critical provider fails? Does our insurance cover agentic AI risks, and are we reviewing this at renewal?
External Assessments, Tabletop Exercises and Crisis Preparedness
- Comprehensive external cybersecurity assessments have traditionally occurred every one to three years, but there is growing momentum toward annual reviews and more continuous monitoring.
- Tabletop exercises should test operational resilience, escalation processes, regulatory reporting, materiality determinations and clarity around decision-making authority.
- Management should lead crisis simulations, with the board receiving after-action briefings or participating as observers where appropriate.
- AI-enabled monitoring and real-time risk scoring may increasingly complement periodic assessments, allowing organizations to identify vulnerabilities and validate controls continuously.
- Questions for the board: When was our last independent assessment? Are we conducting realistic tabletop exercises? Who makes critical decisions during an incident? Are identified weaknesses being addressed and tracked to completion?
Physical Security, Executive Protection and Activism
- Cyber-enabled activism and targeted threats are increasing, with stolen personal information about executives and directors potentially being used for harassment, reputational damage or physical intimidation.
- Executive protection is expanding beyond traditional security to include home networks, residential security, transportation, personal travel and family exposure.
- Documented security assessments are important for determining appropriate protective measures and supporting the tax treatment of qualifying executive security arrangements.
- Employee safety and insider threats also require attention, particularly during sensitive workforce changes or when departing employees retain access to critical systems and AI capabilities.
- Questions for the board: Are we adequately protecting executives, directors and employees? Could cyber threats translate into physical harm? Have we assessed personal and residential vulnerabilities? Are our protection measures aligned with the actual risk?
Geopolitical Risk and Supply-Chain Resilience
- Geopolitical instability is creating interconnected risks across cybersecurity, employee safety, business travel, supply chains and critical infrastructure.
- Regional conflicts and changing security conditions can disrupt operations, threaten personnel and expose dependencies that may not be immediately visible. It was advised that non-essential travel to the Middle East be ceased.
- Organizations need to consider how cyberattacks, activism and physical security incidents could combine to create material business disruption.
- Crisis preparedness should integrate geopolitical intelligence, travel risk management, supply-chain contingency planning and business continuity.
- Questions for the board: Where are our greatest geopolitical exposures? Are we prepared to protect or evacuate personnel? How resilient are our critical supply chains? Could geopolitical or cyber threats create material physical or operational consequences?
Resources
- 2027 Global Risk Map | Global Guardian
Thank you to our partners for making this event possible.
 |
 |
 |
NACD Northern California
Contact Us
Lisa Spivey,
Co-Executive Director
Kate Azima,
Co-Executive Director
programs@northerncalifornia.nacdonline.org
Find a Chapter
By registering for an NACD or NACD Chapter Network event, you agree to the following Code of Conduct.
| NACD and the NACD Chapter Network organizations (NACD) are non-partisan, nonprofit organizations dedicated to providing directors with the opportunity to discuss timely governance oversight practices. The views of the speakers and audience are their own and do not necessarily reflect the views of NACD. |